PCI DSS Audit Latvia: Why Your Business Needs PCI DSS Compliance
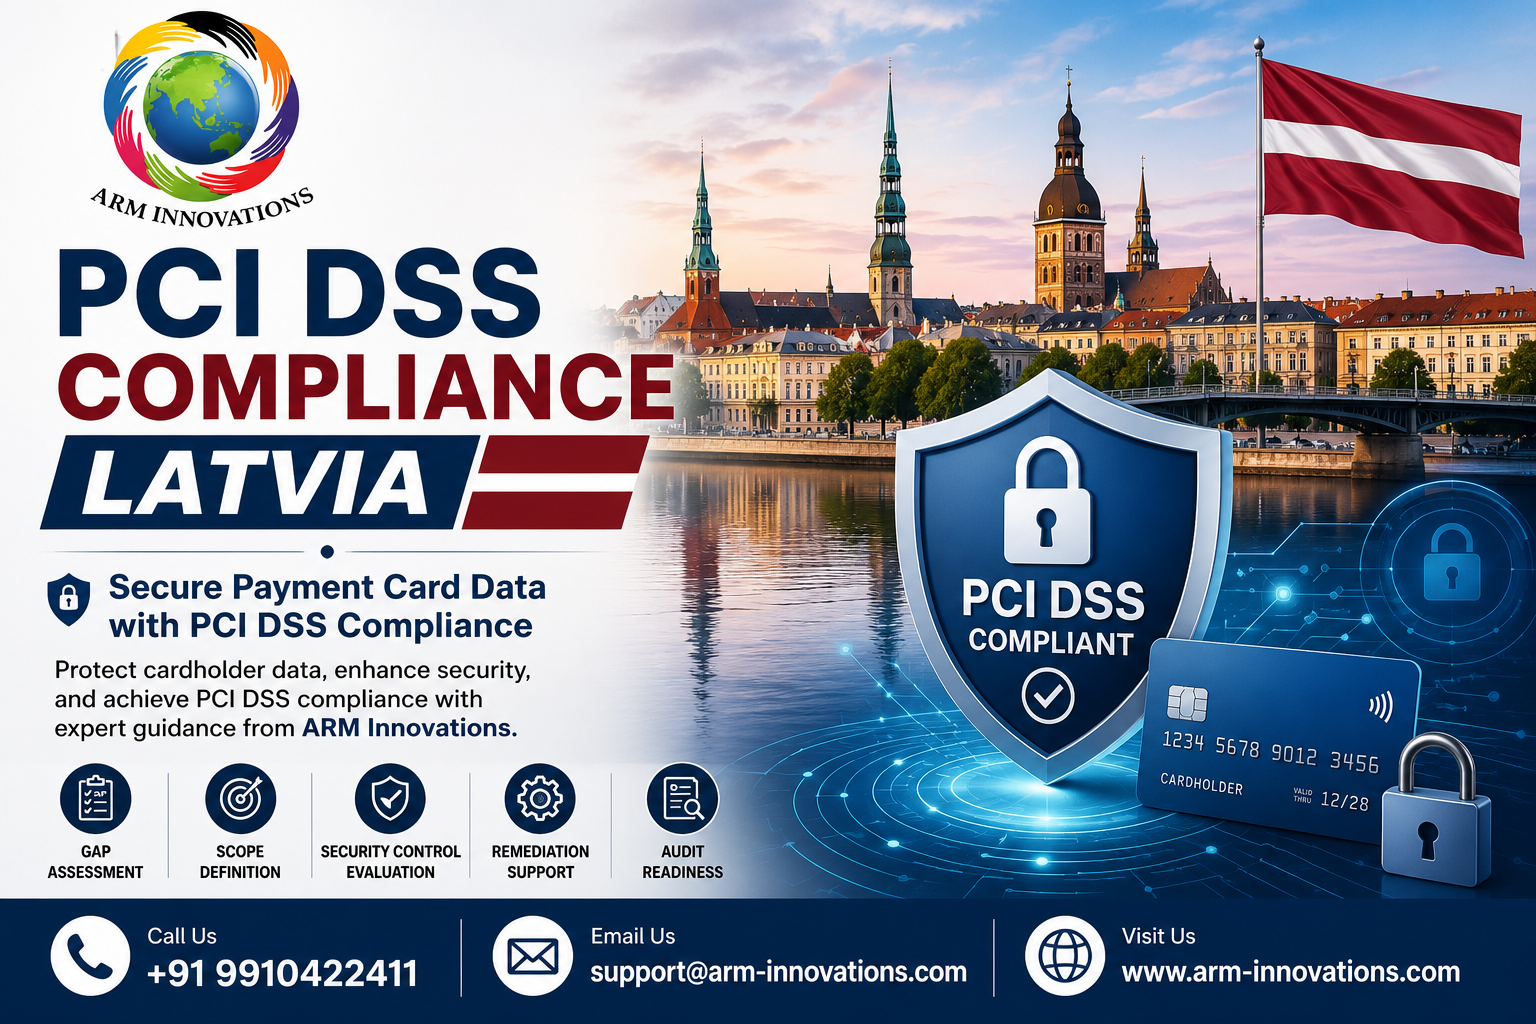
With digital payments becoming the preferred method of transaction across Latvia, protecting customer payment card data has never been more important. Organizations that store, process, or transmit cardholder information are expected to comply with the Payment Card Industry Data Security Standard (PCI DSS). A PCI DSS Audit Latvia helps businesses verify that their payment environments meet these internationally recognized security requirements.
Whether you operate an online store, retail chain, financial institution, healthcare organization, hospitality business, or SaaS platform, a PCI DSS Audit Latvia strengthens cybersecurity, improves customer confidence, and minimizes the risk of costly data breaches.
What is a PCI DSS Audit?
A PCI DSS audit is a formal assessment that evaluates an organization's compliance with the Payment Card Industry Data Security Standard. Developed by the PCI Security Standards Council, PCI DSS provides a framework for protecting payment card information from unauthorized access, fraud, and cyber threats.
A PCI DSS Audit Latvia reviews your organization's technical controls, operational processes, security policies, and documentation to ensure cardholder data is handled securely.
Why is PCI DSS Audit Latvia Important?
As Latvia continues to embrace digital banking and e-commerce, cybercriminals increasingly target businesses that process payment card information. A PCI DSS Audit Latvia enables organizations to identify vulnerabilities before attackers can exploit them.
Key benefits include:
-
Protecting sensitive payment card data
-
Reducing the risk of cyberattacks and fraud
-
Meeting payment provider and acquiring bank requirements
-
Demonstrating commitment to data security
-
Avoiding financial penalties associated with non-compliance
-
Improving customer trust and brand reputation
-
Strengthening overall cybersecurity posture
Who Requires PCI DSS Audit Latvia?
Any organization that stores, processes, or transmits payment card information should undergo a PCI DSS Audit Latvia, including:
-
E-commerce companies
-
Retail businesses
-
Banks and financial institutions
-
Payment gateways
-
Payment processors
-
Hotels and hospitality providers
-
Healthcare organizations
-
SaaS companies
-
Educational institutions
-
Government organizations accepting card payments
Even businesses using third-party payment providers may still have PCI DSS responsibilities depending on their environment.
Key PCI DSS Requirements
During a PCI DSS Audit Latvia, auditors evaluate whether the organization complies with the latest PCI DSS requirements.
1. Secure Network Infrastructure
Organizations must protect payment environments using properly configured firewalls and secure network architecture.
2. Secure System Configuration
Default passwords and insecure configurations should be removed before systems are deployed.
3. Cardholder Data Protection
Sensitive payment information must be encrypted during storage and transmission.
4. Vulnerability Management
Businesses should regularly perform vulnerability assessments, patch management, and malware protection.
5. Strong Access Control
Only authorized users should have access to payment systems using role-based permissions and multi-factor authentication.
6. Continuous Monitoring
Organizations should collect and review logs to detect suspicious activity and respond quickly to incidents.
7. Regular Security Testing
Penetration testing and vulnerability scanning help verify that security controls remain effective.
8. Security Policies and Training
Employees should receive cybersecurity awareness training, and organizations must maintain updated security policies.
PCI DSS Audit Process
A typical PCI DSS Audit Latvia follows these stages:
Define the Audit Scope
Identify all systems, applications, and networks that process or store payment card information.
Conduct a Gap Assessment
Evaluate current security controls against PCI DSS requirements and identify areas requiring improvement.
Remediation
Resolve identified vulnerabilities through technical and administrative security improvements.
Security Validation
Perform penetration testing, vulnerability assessments, and configuration reviews.
Documentation Review
Auditors examine policies, procedures, risk assessments, access records, and compliance evidence.
Final Compliance Assessment
The auditor verifies that all applicable PCI DSS controls have been implemented successfully.
Compliance Reporting
Organizations receive the required compliance documentation to demonstrate adherence to PCI DSS requirements.
Common Challenges During PCI DSS Audit Latvia
Many organizations encounter similar obstacles while preparing for a PCI DSS Audit Latvia, including:
-
Poor asset inventory management
-
Weak password policies
-
Lack of network segmentation
-
Missing log monitoring processes
-
Delayed software updates
-
Excessive user privileges
-
Incomplete compliance documentation
-
Limited employee cybersecurity awareness
Addressing these issues before the audit significantly improves compliance readiness.
Benefits of PCI DSS Audit Latvia
Successfully completing a PCI DSS Audit Latvia offers several business advantages.
Improved Customer Confidence
Customers are more likely to trust businesses that demonstrate strong payment security.
Reduced Cybersecurity Risk
PCI DSS security controls reduce the likelihood of payment card breaches and cyber incidents.
Better Regulatory Alignment
Many PCI DSS requirements align with broader cybersecurity and data protection best practices.
Enhanced Operational Security
Organizations strengthen governance, monitoring, access management, and incident response capabilities.
Competitive Business Advantage
Many enterprise clients and partners prefer working with PCI DSS-compliant organizations.
Financial Protection
Strong security controls help organizations avoid breach-related costs, penalties, and reputational damage.
Best Practices for PCI DSS Compliance
Organizations preparing for a PCI DSS Audit Latvia should adopt the following best practices:
-
Perform regular vulnerability assessments
-
Conduct annual penetration testing
-
Encrypt payment card information
-
Implement multi-factor authentication
-
Continuously monitor security logs
-
Restrict user access based on business needs
-
Apply security patches promptly
-
Train employees on cybersecurity awareness
-
Maintain accurate compliance documentation
-
Conduct periodic internal audits
Treating PCI DSS as an ongoing security program rather than a one-time project helps maintain long-term compliance.
Choosing the Right PCI DSS Audit Partner
Selecting an experienced cybersecurity partner simplifies the PCI DSS Audit Latvia process.
Look for a provider that offers:
-
PCI DSS compliance consulting
-
Penetration testing services
-
Vulnerability assessments
-
Compliance gap analysis
-
Security remediation support
-
Documentation assistance
-
Continuous compliance monitoring
-
Industry-specific expertise
A knowledgeable audit partner helps organizations achieve compliance efficiently while strengthening their overall cybersecurity posture.
Conclusion
Protecting payment card information is essential for every organization handling electronic transactions. A PCI DSS Audit Latvia enables businesses to identify security weaknesses, improve compliance, and protect customers from payment card fraud.
By implementing PCI DSS security controls, conducting regular assessments, and partnering with experienced cybersecurity professionals, organizations can meet international compliance requirements while building trust with customers and business partners. Investing in a PCI DSS Audit Latvia is not only a compliance requirement but also a strategic step toward stronger cybersecurity and long-term business resilience.